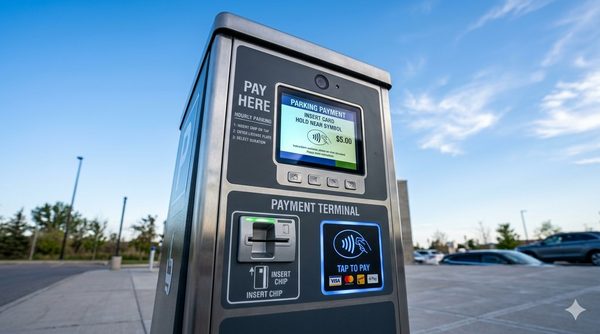
PCI-validated point-to-point encryption gets sold to parking operators as a compliance product, and on that basis the pitch is strong. A merchant moving from SAQ D to SAQ P2PE goes from 329 self-assessment questions to 21 — close to a 90% reduction in the controls being attested to. For an operator running unattended pay stations across multiple sites, that is a material reduction in annual assessment burden.
What gets discussed far less often is that the same decision reshapes your processor relationship. A P2PE deployment is not only a security architecture. It is frequently a commercial structure, and the two are easy to conflate at signature.
The Distinction That Actually Governs Scope
Start with the difference that determines whether you get the scope reduction at all.
PCI-validated P2PE means the full solution — the point-of-interaction device, the encryption, the key management, the decryption environment, and the operational procedures — has been assessed by a Qualified Security Assessor against the PCI SSC’s P2PE program and appears on the Council’s list of validated solutions.
Non-validated P2PE, sometimes marketed as end-to-end encryption, may be cryptographically sound and still deliver no scope reduction, because scope reduction is an artifact of the validation and the accompanying P2PE Instruction Manual, not of the encryption itself.
There is a trap here that catches operators regularly: a processor appearing on the validated-solutions list does not mean the specific configuration you are buying is the validated solution. The terminals you are deploying may be supported models within that solution while your actual deployment sits outside its validated boundary. The question to put in writing is not “are you P2PE validated” but “is the exact solution, listing number, and device configuration we are deploying the validated one, and will you provide the P2PE Instruction Manual for it.”
If the answer arrives with qualifications, you are buying encryption, not scope reduction.
Where the Contract Consequence Lives
In a validated P2PE solution, the decryption environment belongs to the solution provider. Card data leaves your pay station encrypted to keys you do not hold and cannot hold — that is precisely why your environment falls out of scope. The keys are injected into the device under the solution provider’s key-management procedures, usually at a certified injection facility.
That architecture has an obvious commercial consequence. If decryption is coupled to processing, then changing processors means re-keying the estate. Re-keying an unattended parking estate is not a configuration change. Depending on the device and the solution, it can mean pulling terminals for injection at a facility, staged site visits, or replacement hardware — across every lane and every pay station.
This is the part that belongs in the procurement conversation and usually is not. The compliance benefit is immediate and the switching cost is deferred, which is exactly the shape of a decision people underestimate.
Decoupled P2PE Exists
The market has responded to this, and operators should know the option exists before assuming lock-in is inherent to the model.
Some providers have deliberately separated P2PE from payment processing. Bluefin’s Decryptx is built around decoupling decryption from the processor relationship, offered through gateways, processors, and software vendors. TokenEx’s validated solution is positioned to work across gateways, processors, and PCI PTS-listed terminals rather than binding to one acquirer.
The trade is real in both directions. A processor-coupled solution is typically cheaper, simpler to procure, and supported end-to-end by one vendor. A decoupled solution costs more and adds a party, and it preserves your ability to move processing without touching the hardware. Which is correct depends on how likely you are to re-bid processing inside the terminal’s service life — and given typical pay station lifecycles, the honest answer for most operators is “at least once.”
What to Put in the Contract
Five items, none of which are exotic, and all of which are cheaper to negotiate before signature than after:
Name the validated solution. The listing name, the listing number, and the device models, written into the agreement rather than referenced from a datasheet.
Require the P2PE Instruction Manual as a deliverable. The PIM defines what you must do operationally to stay inside the validated solution. Your scope reduction depends on following it, and you cannot follow a document you were never given.
Price the exit before you need it. Ask directly: if we move processors in year three, what happens to these terminals? Get the re-keying process, the per-device cost, and the site-visit requirement in writing. A vendor unwilling to quote this is telling you something.
Separate the terms. Where the commercial structure allows, avoid a single agreement whose termination provisions govern both processing rates and decryption services. Coupled terms mean a rate renegotiation carries an implicit hardware threat.
Confirm key-injection logistics. Who injects, where, what the turnaround is, and what a mid-life device replacement looks like operationally. For unattended parking equipment this is the difference between a swap and a truck roll.
The Right Framing
P2PE is genuinely good technology, and for unattended parking it is close to the ideal application — high transaction counts, distributed devices, no staff at the point of interaction, and a card data environment that is expensive to defend if it stays in scope.
The point is not that operators should hesitate. It is that the scope reduction is the benefit being marketed, and the processor coupling is the term being bundled with it. Evaluate them as two decisions, because that is what they are, and the second one lasts as long as the hardware does.